
Written guide
Roles, records, pages and menus
Cedar & Form needs Maya Chen to handle incoming enquiries. She should read, create and update lead records, without deleting them, approving decisions or editing page components. Her navigation should lead to the enquiries work, while the administrator retains a separate account for configuration. This is the starting permission profile; you will also build a page-editor alternative and practise removing access.
A role supplies permissions. A group supplies membership and can grant roles to its members. A person's effective access can therefore come from direct role assignments and several groups. Looking only at the role you are editing misses those other sources. Before changing Maya's account, open her profile in User Management and note her direct roles, group memberships and inherited roles. Use a training account without Owner, RootAdmin or RootUser privileges for the colleague side of this exercise.
Record permissions describe actions on records. Page permissions describe actions on components. Menu access describes which screens are available. These controls answer different questions: a visible Leads link does not by itself authorize changing a lead; permission to update records does not by itself add that link to navigation. A role name such as cedar-enquiry-editor is an identifier, not a rule restricting records to Cedar enquiries. Collection access, ownership, workflow state and server authorization can impose additional conditions.
Use a training organisation containing disposable lead records and a draft page. Create the records through the CRM course or your normal Leads form and give the lead a recognisable training name such as Cedar permission practice. Avoid deleting a real lead merely to demonstrate a denied action. Keep an administrator session available in one browser profile and Maya's session in another so that each result belongs to the correct identity. Record the organisation shown in each session before starting.
The finished example will contain a saved custom role, a group granting that role, Maya's membership, and observed allowed and denied actions in Maya's fresh session. A list of selected checkboxes is an intermediate result. The colleague's actual experience is the final result of the exercise.
System roles and custom role creation
Open Configuration → Role & Permission. The Role Manager sidebar lists available roles; New Role opens a blank custom role in the main editor. On a narrow screen, use Roles to reach the sidebar. Always read the selected role name before changing permissions. The separate Menu Access entry opens the same manager in its menu view and can initially select the built-in User role; it does not mean your custom role is selected.
First select a system role and inspect its badge. Its name, description, record permissions and page permissions are read-only in this editor. Menu access remains editable. The read-only banner therefore has a specific scope: it does not disable the menu panel. Do not change a shared system role for this first exercise, because its menu changes may affect many existing colleagues.
Now create the Cedar role:
- Click New Role. Enter
cedar-enquiry-editorin Name. - Enter
Cedar & Form enquiry staff: read, create and update leads; no deletion or page editingin Description. - In What this role can do with records, select Read, Create and Update. Leave Delete, Review and Approve clear.
- Expand What this role can do on pages and leave its four permissions clear.
- Click Create role at the bottom of the form. Wait for the save to finish. If an error appears, keep the form open and correct it before continuing.
- Select another role and return to
cedar-enquiry-editor, or reload the manager and select it again. Read back its description and the three selected record permissions.
Names accept letters, numbers, hyphens and underscores. Spaces and punctuation such as & are not accepted in the identifier; use the description for readable wording. The saved name is immutable in this editor, while a custom role's description remains editable. Choose the identifier before assigning it to groups. If you need a different identifier later, create a replacement role, transfer intended assignments and test the replacement before retiring the old assignment.
A successful first save changes the primary action from Create role to Save role and makes Name read-only. The sidebar also has Save for custom roles. Prefer the form's primary action for creation because it presents name validation with the form. Do not treat switching roles or closing the screen as a save.
System roles have predefined capabilities. Editing their menus creates or updates the organisation's saved representation of that role; it does not rewrite the platform's global built-in definition. For a job with different record or component capabilities, make a custom role instead of trying to unlock disabled system-role checkboxes.
Record permissions and job responsibilities
The six record permissions let you describe different responsibilities without assuming that everyone who can read information should also change it. Read opens and views records. Create adds records. Update changes existing records. Delete removes records. Review concerns items waiting for a decision, and Approve concerns signing those items off. The editor exposes separate checkboxes; selecting Review does not automatically select Approve.
Return to the saved cedar-enquiry-editor role. Read, Create and Update should be selected, and the section should report three grants. That combination describes Maya's intended work. It does not identify a particular collection and does not select the CRM screen. Leave the role at these three permissions while you configure navigation in the following section.
For a read-only variation, create cedar-enquiry-reader with only Read selected. Use the description Cedar & Form enquiry observation; no record changes. Save it, then give it only the menus needed for the intended reading task. Test with a second training account or replace the editor role temporarily; adding reader to an account that already has editor will not remove the editor's update grant.
For a review workflow, create cedar-enquiry-reviewer and choose Read and Review initially. Open a training item already waiting for review in a module that implements that workflow. Review and approval are meaningful only where the module has corresponding states and actions. If the colleague must also sign off, add Approve, save and repeat the same item-stage exercise with a fresh session. Do not assume an approval queue appears simply because the checkbox is selected. Nor should you grant Create, Update or Delete by habit when the task is only reviewing.
A practical decision table for the main Cedar role is:
| Operation | Intended result | Observation to keep |
|---|---|---|
| Open a training lead | Allowed | Lead detail and matching training identity |
| Create a training lead | Allowed | Saved record visible after reload |
| Change its training note | Allowed | New value still present after reload |
| Delete a disposable training lead | Denied | Refusal or absent action, plus record still present |
| Sign off a workflow item | Denied for this role | Refusal in a workflow that actually supports approval |
A hidden action establishes a UI outcome; it does not alone establish that the server rejects a direct request. In an authorised test environment, use the same module's documented API with the colleague's own credentials to check the denied operation as well. Do not copy an administrator request with administrator credentials and call it a colleague test.
If Update still works after removing it from this role, inspect every role and group applied to the account, refresh the account's session, and examine collection or module rules. If a permitted save fails, read the error before changing permissions: a required field, invalid record state or missing collection-level rule can fail independently of the role.
Page-component permissions and the editor role
Expand What this role can do on pages. The four permissions are View, Add, Remove and Configure. They refer to seeing components, placing new components, taking components off a page and changing component behaviour. They are separate from record Create, Update and Delete. A person who maintains lead data does not need component editing capabilities merely because the data appears on a page.
Keep all four clear on cedar-enquiry-editor. For the alternative Cedar page-maintenance job, create a separate custom role named cedar-page-editor, with description Cedar & Form draft page maintenance. Give it View, Add and Configure, leaving Remove clear for the first test. Choose any record permissions only after considering the draft-page workflow you are authorising; page components are stored and loaded through application services, so the component controls alone are not a promise that every editor action will succeed.
Save the role and give it the Build Studio menu entries needed for the exercise. Assign it to a separate training colleague or replace Maya's earlier assignment temporarily so that the test does not combine unrelated grants. Use an unpublished practice page with a heading Cedar component practice and an expendable text component. Record the page's initial saved state in the administrator session.
Sign in as the page editor. Open the draft page and try viewing its components. Add a text component containing Training hours: Monday to Friday, then change its configuration through the actual component controls. Save the page using the editor's own save action, reopen it and read back the value. Role saving and page saving are separate operations: saving permissions does not save a page draft, and saving a page does not change a role.
Next attempt to remove the expendable component. The intended role profile lacks Remove. Observe the actual control and outcome. If removal succeeds, stop and inspect the account's other grants and the editor's enforcement rather than claiming that the role worked. If an action is simply unavailable, record that UI result and keep server enforcement as a separate test.
To demonstrate a complete page-maintainer role, the administrator can add Remove, click Save role, refresh the colleague's session, and repeat removal on the expendable component. Reopen the page to confirm the persisted result. Use a new expendable component if the first attempt unexpectedly succeeded.
None of these four labels says Publish. Publishing can involve other menus, organisation configuration and deployment-specific authorization. Teach publication through the Build Studio course's explicit save, preview and publication steps, then check that action independently for the colleague. A visible editor or a Configure grant is insufficient evidence of publishing permission.
Appmint, Business Made and Mobile app menus
Select cedar-enquiry-editor and scroll to Menu access. The tabs are Appmint, Business Made and Mobile app. The application you opened the editor from places its web tab first; Mobile app remains last. Each tab shows a catalogue of screens grouped into sections, with a selected count. The item also displays its route path. Read both the label and path when similar labels appear in different areas.
For the enquiry example, open the Appmint tab, find Leads in the CRM section, and select that item. There are other Leads entries for other modules, so use the CRM grouping and displayed path to choose the intended one. Expand only the work menu required by your exercise. Selecting a section heading toggles its items together; selecting a single row changes that route. When two labels point to the same route, their selection can move together because the stored grant is the route, not the display label.
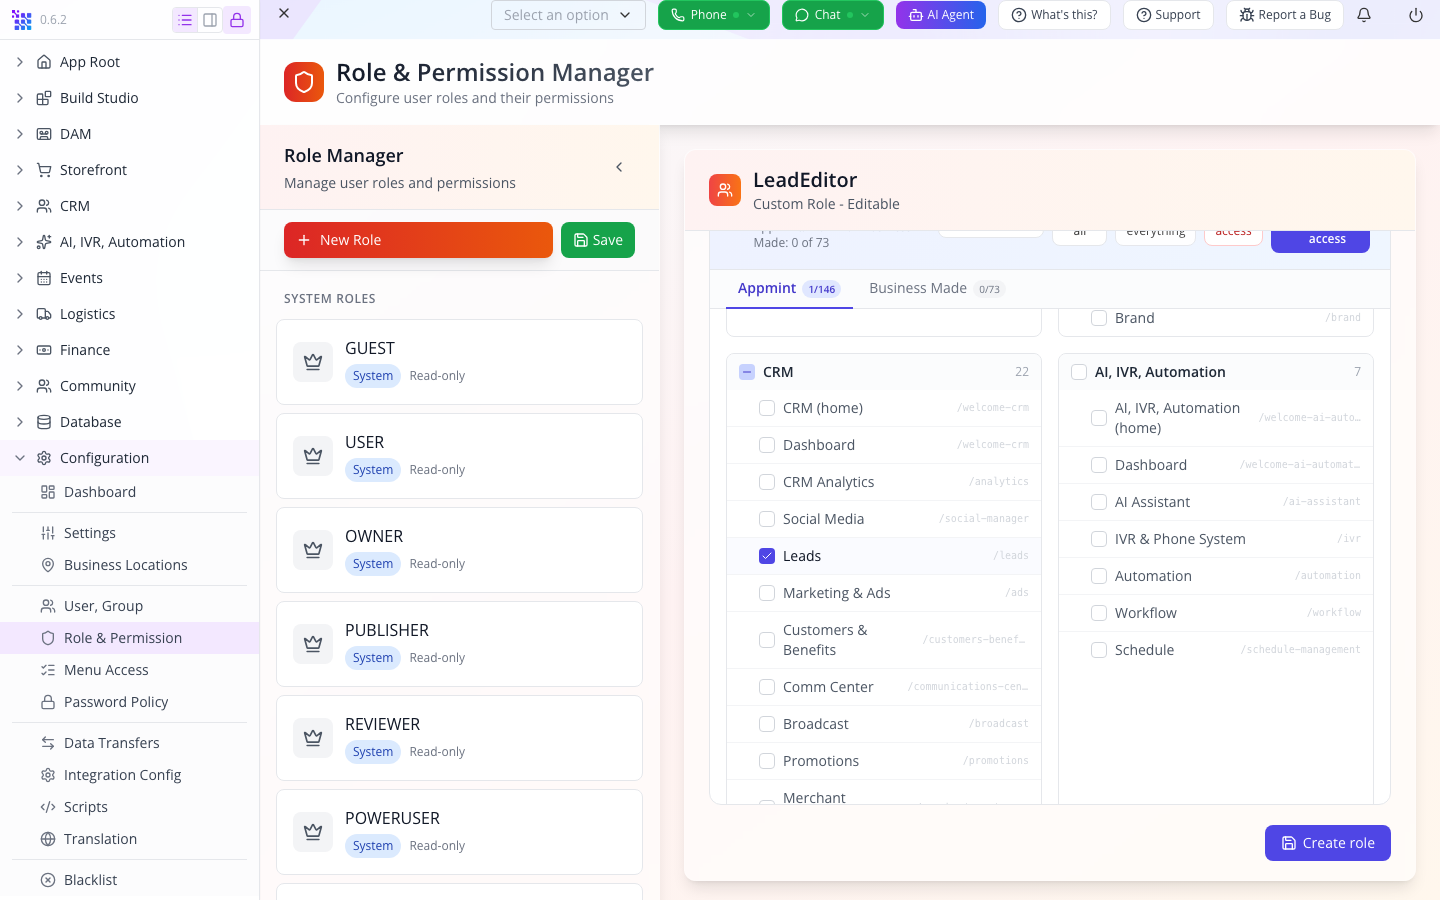
Historical LeadEditor draft with CRM Leads selected. This is a different role name from the Cedar exercise; Create role is still visible, so the image does not establish a saved grant. It shows how the CRM grouping and route distinguish the intended Leads screen. The older capture shows the two web-app tabs; use the current Mobile app controls described below rather than assuming that older catalogue is complete.
Open Business Made and examine its catalogue separately. Select the actual Business Made destination only if this colleague performs a corresponding job there. Return to Appmint and confirm the Leads selection remains. A tab change does not discard the other tabs' route selections: all three contribute to one role menu profile. Save only after reviewing the combined selection.
Mobile has a particularly important starting condition. Until the role names a mobile path, the mobile panel describes No mobile restriction. Selecting web routes alone therefore does not mean the phone app is denied. On Mobile app, select the specific available mobile work item required for the training account, using the actual displayed catalogue. The first mobile selection changes that app to a selected-items profile. Keep the item name and route in your exercise notes because the catalogue comes from the installed SDK and may differ by release.
If the job has no mobile requirement, do not invent an empty-tab deny rule: a cleared mobile selection returns the no-restriction condition for that role. Use the organisation's appropriate account/device policy and test the actual phone app. The global No access control discussed next applies across the role and is not a way to deny only one app while retaining selected web access.
Click Save menu access, wait for the response, and reopen this same role. Read the three tabs again. Finally sign in as Maya and inspect the relevant application. The editor's selected count describes configured routes; the application may also apply account type, organisation features, other roles and route guards. A mobile device may hide more than the allowed mobile selection, so use an actual authorised mobile session for the phone outcome.
If a newly granted screen does not appear, first confirm the correct role and organisation, then the exact route and app tab, then the person's current roles. A feature unavailable to the organisation will not become available merely because its menu item is selected. Avoid broadening every menu just to solve a single missing entry.
Group grants and direct role assignment
Once the editor role has a saved menu profile, assign it through a group. Open User Management → User Groups and create or edit cedar-enquiries. Use Description Cedar & Form enquiry handling team. In Roles this group grants, add cedar-enquiry-editor. Select Maya's training account by its controlled email address in the membership controls. Click Add 1 to stage Maya as the selected member, then click Create group or Save group to persist the change.
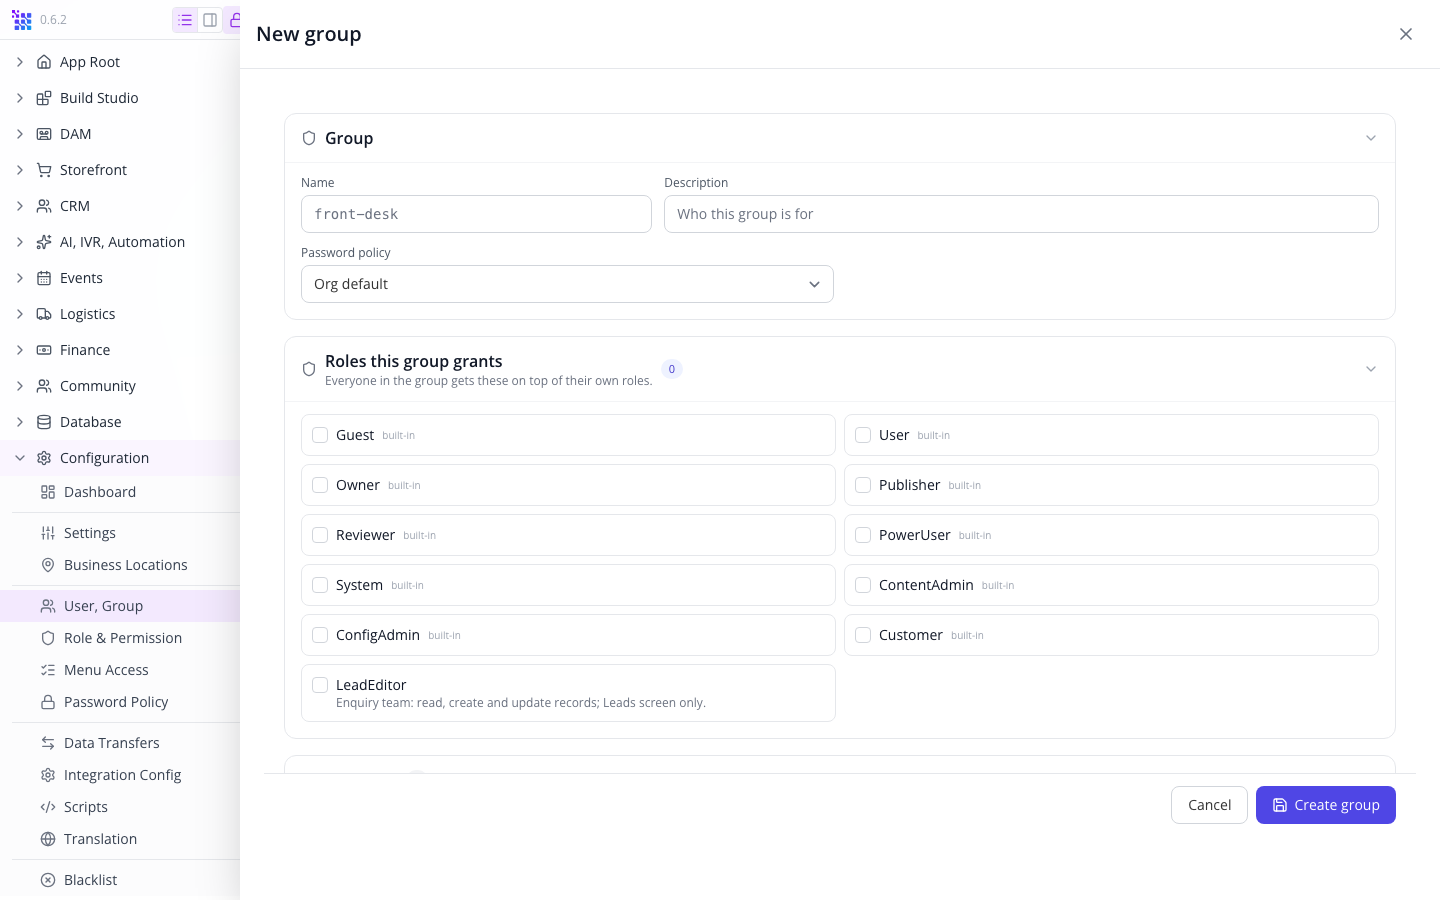
Historical unsaved group form: LeadEditor is available but unchecked, and the selected-role count is zero. The front-desk text is the name-field example, not proof of an existing Cedar group. Select your actual saved role and intended member, save, and reopen both the group and the person to prove the relationship.
The group operation saves the group and then applies added or removed explicit memberships to the affected users. Reopen both the group and Maya's profile afterwards. A group-save message should not be the only evidence for a membership change; a later membership request can fail separately. The saved result should show the named role on the group and Maya as an explicit member, with the corresponding inherited role in her profile.
Groups can also show members present through a role relationship. The group editor distinguishes these from explicitly added members, and they cannot be removed by the explicit-member control. If Maya appears through such a relationship, trace that underlying assignment rather than repeatedly trying to remove her from the visible list. Built-in group roles can be fixed rather than freely removable. Work in the custom Cedar group for this lesson.
A direct role assignment is useful for a deliberate individual exception. The current modern profile supports removing certain direct roles for an eligible administrator, but it does not expose a corresponding general Add role control. Do not search indefinitely for one based on an older screenshot. Use the group workflow for the ordinary visual lesson. For administrators with an authorised API workflow, the application service exposes this advanced alternative:
<configuredAPI{
"email": "<Maya's controlled training-account email>",
"roles": ["cedar-enquiry-editor"]
}Use the organisation and authentication mechanism already configured for your approved API client. The base URL placeholder is not a hostname to paste literally. The email placeholder must be replaced with the actual training account, and the role must already exist under the exact saved name. Keep tokens and session headers out of screenshots and course notes. This request changes access when sent; submit it only for the training assignment you intend.
Read the API response, reopen Maya's profile, and distinguish the new direct assignment from group inheritance. To remove that direct grant through the same API workflow, use POST <configured API base>/profile/user/role/remove with the same email/roles payload. An HTTP success alone is insufficient for the lesson: follow it with the refreshed profile and the colleague's fresh sign-in.
Avoid leaving both a direct assignment and a group grant accidentally. They can be intentional, but removing one will not demonstrate full revocation while the other remains. Record why each source exists, then choose one source for the basic Cedar exercise.
Allowed screens, denied actions and fresh sessions
Now use Maya's separate browser profile. Sign out and sign back in after the administrator's role and membership saves, or use the product's supported session refresh and inspect the returned identity. The current profile carries resolved roles and permissions, so an older open tab may not reflect a recent change.
Start with the allowed workflow. Open the Appmint CRM Leads screen through the visible menu. Open Cedar permission practice, read its details and make a harmless change to its training note. Save the lead with the module's own save action. Reload or reopen it and read the changed value. Create a second disposable lead through the normal form, supplying the required values shown by that form, and reopen it after saving. These outcomes demonstrate the intended Read/Create/Update path under the actual account.
Next test the intended boundaries. Inspect Delete on a disposable lead. If it is absent or disabled, record that exact UI result. If it is available, attempt deletion only on the disposable record and observe whether the server accepts or rejects it. Check the record afterwards from the administrator session. An unexpectedly successful delete is a failed restriction test, even if the role editor still displays an unchecked Delete box.
Test a restricted screen both through navigation and through its actual URL. Copy the administrator's URL for a training-only configuration destination, then open it in Maya's browser profile. Observe the route guard, displayed screen and any loaded data. Do not invent a URL from its sidebar label or assume hiding a menu prevents a direct URL. Record both the menu result and the direct-navigation result. If the screen opens, inspect other assigned roles and report the remaining authorization issue before calling the role ready.
Repeat the relevant component tests only with the cedar-page-editor alternative. Keeping those tests separate makes it clear which role grants which operation. Where an approval workflow exists, attempt the real review and approval actions at the correct workflow state. A missing workflow or an invalid test item cannot establish that Approve is denied.
Use a simple observation sheet with columns for account, organisation, role sources, application, action, intended result, actual result and saved-state check. Enter what happened: for example, Update allowed; training note remains after reload, or Delete visible; server refused; record remains. Avoid substituting checkbox unchecked for an action result.
If the UI fails before it reaches the permission check, resolve the actual issue first. A network failure, missing record, invalid required field, feature entitlement or expired session is not evidence of a denied permission. Re-run only the affected case after correction. A completed permission profile has both successful intended work and observed boundaries; neither side alone is enough.
Access removal and role maintenance
For the final exercise, remove the source of Maya's editor access. In the administrator session open cedar-enquiries, remove Maya's explicit membership, and Save group. Reopen the group and her profile. If she has a direct cedar-enquiry-editor assignment, remove that separately through the available direct-role removal action or the authorised API method from the previous section. The profile's removal controls are restricted and protect roles such as Owner and system roles; do not use a privileged account as the disposable subject.
Refresh Maya's session and repeat the same Leads screen, direct URL and training-record action cases. Use the same observation sheet so the before and after results are comparable. Confirm the remaining role sources rather than expecting an account with baseline User permissions to become completely unable to sign in. Removing one business role is not equivalent to locking the account or revoking every device.
If access remains, work through its sources in order. Reopen the account after the save, check direct roles, check every group, identify any all-access role, then sign in afresh. Check whether the intended restriction was a menu selection, a record action or a collection/module rule. An inherited grant cannot be removed by deleting an unrelated direct grant. A No access menu test also has different semantics from removing an update permission.
After the revocation exercise, restore only the assignment that Cedar intends to retain. Reopen the group, refresh Maya's session and repeat one allowed and one denied case. Keep the administrator recovery session separate throughout; there is no need to grant Maya Owner to make the workflow pass.
For ongoing changes, edit a role according to a named job responsibility. Before changing a shared role, identify its directly assigned users and granting groups through the available directories. Test the proposed profile with a training account first. Save one coherent change, read it back and re-run the affected operations in each application the role serves. A mobile-only adjustment still deserves a mobile test, and a web-menu change does not establish record enforcement.
If a new responsibility should apply to only some members, create a separate custom role or group assignment instead of broadening the shared role silently. For an identifier change, create the replacement role and migrate assignments deliberately; the Name field on the existing saved role is not editable. Keep the old assignment until the replacement's intended operations work, then remove the old grant and repeat the denied cases to catch permissions it had contributed.
The Cedar exercise is complete when the saved role and group explain Maya's effective access, the intended actions persist their results, denied actions actually fail in the tested paths, and removing the grant changes her refreshed access as expected. Keep any untested application, physical device, workflow or API case as an open item in the observation sheet rather than assuming that one web screenshot covers it.
BusinessMade Roles and Permissions: Record, Page and Menu Access — supporting guide
BusinessMade route: Admin → Roles & permissions (/admin/roles).
This route mounts the shared account/access component, checked against BusinessMade's route registry. Use the Business Made menu-access tab for BusinessMade screen permissions. Appmint Mobile access remains separate; a staff account, HR employee and Device Hub are not interchangeable identities. Main demonstrations stay in BusinessMade; any optional Studio Manager branch is explicitly identified.
**Written course script · documented draft **
Overview
Why this matters
BusinessMade separates what people can do with records, what they can change on pages and which screens they can open. We'll configure those controls, assign a role through a group and check the result using a colleague's account. We'll also look at mobile access, presets and how to remove a grant without overlooking another source of access.
Preparation
Keep administrator and ordinary colleague sessions in separate browser profiles, in the same training organization. The colleague must not have Owner, RootAdmin or RootUser privileges. Have a disposable customer. A draft website page is needed only for the optional shared Build Studio permission branch. Inspect existing direct roles and groups before starting; these are cumulative sources of access, with additional menu-policy exceptions described below.
1. Find the role editor and distinguish system roles
Open Admin → Roles & permissions. Select a system role and inspect its badge. Show that name, description, record and page permissions are read-only while its menu panel remains editable. Do not change a widely assigned system role for the practice exercise.
Why this matters
System roles have built-in capabilities. Their menu access can still be customized for this organization. For a different set of record or component actions, create a custom role.
Use Roles to reopen the sidebar on a narrow screen. If entering through Menu Access, inspect the selected role: that route can start on the built-in User role rather than the custom role you intended.
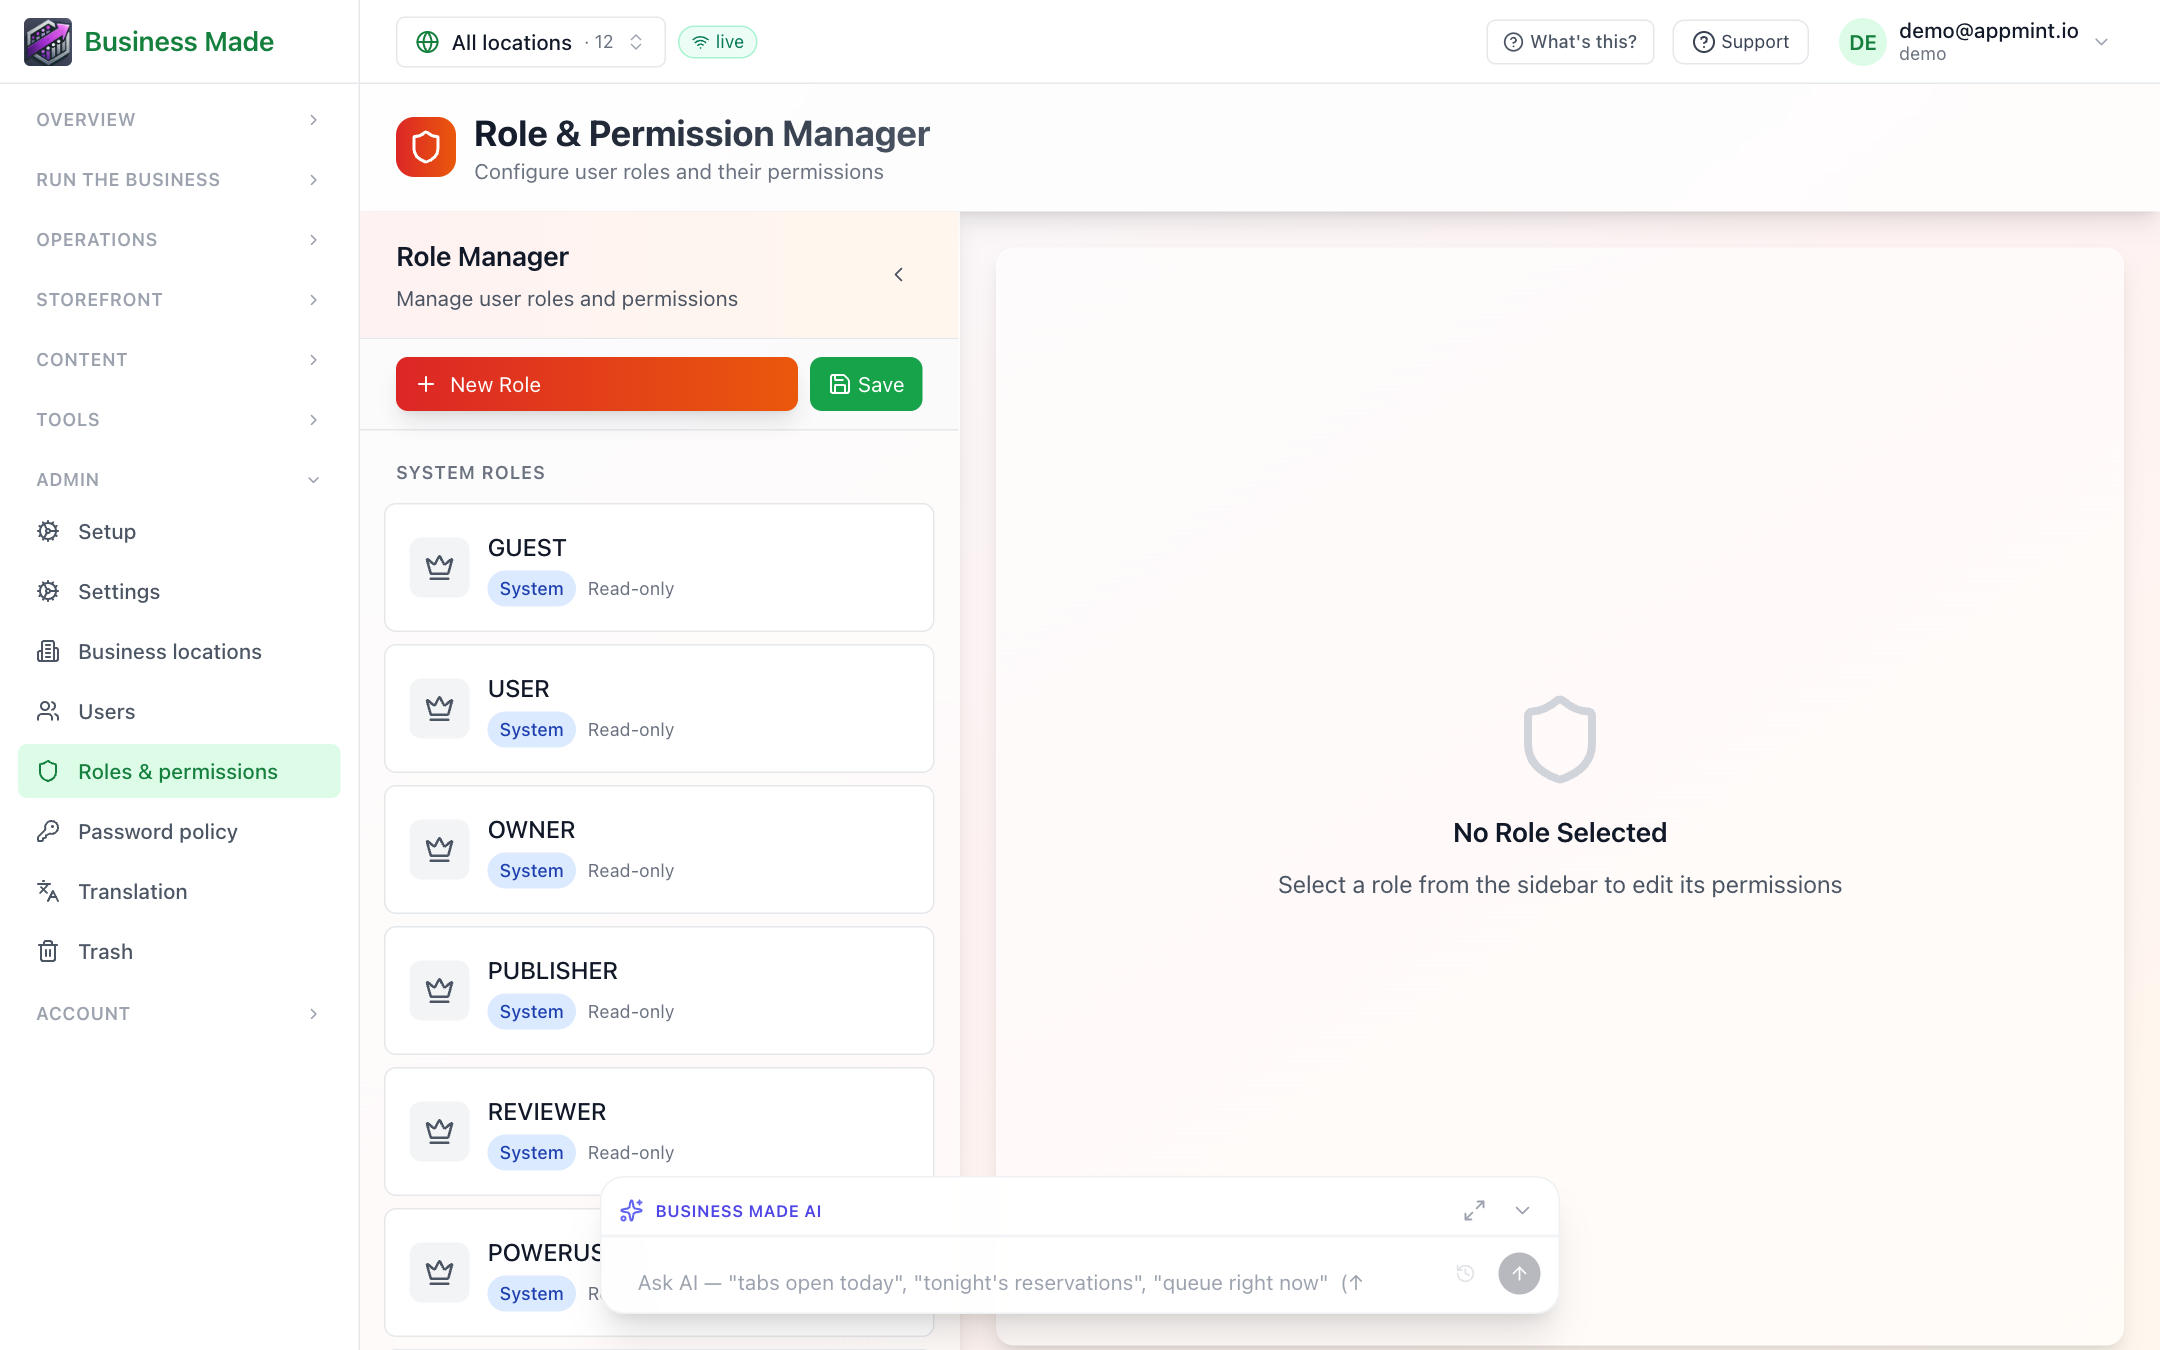
Find your place: the list on the left contains role definitions; it is not a list of staff accounts. The empty main panel means no role is selected. Select an existing definition to inspect it, or New Role for the custom example below. This retained image predates the current menu-tab layout; it is used only to identify the role list and entry point, not as proof of a saved custom role. Do not use Owner as the ordinary employee test account.
2. Create and save a custom role
Choose New Role, enter Name counter-record-editor and a description identifying counter staff who read, create and update records. In What this role can do with records, select Read, Create, Update. Leave Delete, Review and Approve clear. In What this role can do on pages, leave the four component permissions clear. Choose Create role, wait for the result, switch away and reopen it.
The saved name becomes read-only; its description remains editable for custom roles. Names accept letters, numbers, hyphens and underscores. A name describing counter staff does not limit all record access to one collection. Collection rules, record ownership, workflow state and server authorization are separate constraints.
3. Compare record responsibilities
Why this matters
Read, Create, Update and Delete separate ordinary record operations. Review and Approve are distinct decisions where a module implements that workflow. Selecting Review doesn't automatically select Approve or create an approval queue.
Create a reader alternative with Read alone. Do not assign it on top of the editor and expect Update to disappear. Test it with a separate account or replace the existing grant. For a reviewer alternative, select Read and Review, assign it to the controlled account and use an actual item waiting for review. Add Approve only for the sign-off branch, save and refresh the account before repeating.
Demonstration outcome
The editor reads a training customer, creates a disposable customer and saves a non-sensitive field change through the Customers & Benefits editor. Delete should be refused or unavailable; record the actual outcome. If the action is hidden, separately test server refusal through the same documented API with the colleague's credentials. A required-field error or network failure is not a permission-denied result.
4. Advanced shared capability: page-component permissions
This optional branch is for a person who also maintains the organization website through Appmint Build Studio. It does not add a website editor to BusinessMade or grant POS operation through a page checkbox. Keep it separate from the counter role. Create cedar-page-editor. Under What this role can do on pages, select View, Add and Configure, initially leaving Remove clear. Choose any necessary record grants explicitly for the page workflow, and save the role. Configure the required Build Studio routes in its menu profile.
Why this matters
These controls concern website page components, not customer records or POS sales. We'll test this role on a draft page with an expendable component, so the result belongs to the capability we're configuring.
Assign the role to a separate ordinary account. Open the draft page, add a text component, configure its text, save the page and reopen. Attempt removing the expendable component and record whether the control or server refuses it. If removal succeeds unexpectedly, investigate other grants or enforcement; do not describe that result as success.
For the full-maintainer alternative, enable Remove, save, refresh the colleague identity and repeat on a disposable component. The four labels do not include Publish. Publication needs its own Build Studio action and authorization check.
5. Choose Appmint, Business Made and Mobile menus
Open Menu access on the intended saved role. Show the Appmint, Business Made and Mobile app tabs. Select Business Made, then Customers & Benefits, checking /crm/customer-groups as well as its label. Add only the other screens needed for the counter role. Section-heading selection toggles its children; a single row selects its route. Labels sharing one route may move together.
Switch to Appmint only when the person also needs Studio Manager access. Return and confirm the Business Made selection remains. The tabs contribute to one profile rather than three discarded drafts.
Important mobile explanation
An empty mobile selection is shown as No mobile restriction. Selecting web screens doesn't deny the phone app. Choosing a mobile item changes this role's mobile profile to the selected items.
Select the actual required mobile route from the installed catalogue. Save and inspect it on a controlled mobile account. If mobile is not part of the job, do not describe an empty mobile tab as a deny rule. Global No access is not a mobile-only restriction.
Choose Save menu access, wait for the result and reopen the role. A selected count establishes configured routes, not successful application access; features, account type and other role logic also influence what the person sees.
6. Compare presets and broad-access controls
Use an unassigned disposable custom role for this comparison. Explain each control beside its actual result rather than narrating all four while clicking unpredictably.
| Control | What the editor changes | Required check |
|---|---|---|
| Preset… | Replaces the current route selection with preset paths | Review every tab and reapply needed custom choices |
| Select all | Selects current catalogue paths across all three apps | Read all three counts; this is an explicit list, not future unrestricted access |
| Allow everything | Clears explicit include/exclude restrictions | Built-in defaults and account rules can still affect runtime behavior |
| No access | Stores an explicit deny-all marker | Test an ordinary account; this is not account locking |
Why this matters
Select all saves today's list. Allow everything removes the role's explicit menu restriction. No access stores a deliberate denial. Those are different policies, even when two screens initially look similar.
Demonstrate explicit route → Save → reopen; No access → Save → reopen; Allow everything → Save → reopen. Restore the intended list before assignment. An empty resolved preset becomes explicit No access in this editor. Ordinary explicit menu denial can override other ordinary menu grants; privileged identities are handled earlier, so an owner account is unsuitable for proving denial. Landing or welcome screens can remain reachable.
7. Save without accidentally combining draft changes
Explain with the actual controls visible
Save role and Save menu access are separate buttons, but they currently save the same role object. If you change both areas before saving, either operation may persist both drafts.
Finish record/component changes, Save role, reopen, then finish menus, Save menu access, reopen. System roles use the menu save route because the other controls stay locked. Show an actual save error if one occurs, correct it and read the saved state again. Switching roles or closing the panel is not a save operation.
Do not illustrate this with a text warning slide; show the two controls and the shared saved role in a brief focused illustration, followed by the actual clean save sequence.
8. Assign the role through a group
Open Admin → Users → User Groups, create or edit counter-team, and select counter-record-editor under Roles this group grants. Find the controlled colleague by email, choose Add 1, then Create group or Save group.
Reopen group and user profile. Confirm the role on the group and explicit membership on the person. The group save and membership synchronization use separate operations; a later failure can leave a partial result.
Why this matters
Add stages the selected person. Save applies the group change. I'll check the group and the person's profile so a partial membership failure doesn't go unnoticed.
Rows marked as present through a role cannot be removed as ordinary explicit membership. Trace that role assignment. A fixed built-in group role is not a freely editable custom group grant.
9. Advanced alternative: direct role assignment
The modern profile exposes eligible direct-role removal but no general Add Role button. Teach the group route for ordinary UI work. For an authorized administrative API client, the current service exposes:
<configuredAPI{
"email": "<controlled colleague email>",
"roles": ["counter-record-editor"]
}Use the configured organization's authentication and actual saved role name. Keep credentials private. Inspect the response, reopen the user profile and distinguish direct assignment from inherited roles. The matching removal endpoint is POST <configured API base>/profile/user/role/remove with the same payload shape.
Why this matters
A direct assignment is an individual grant. Removing group membership won't remove this second source. We'll retain only the source intended for this example.
Do not execute the literal placeholder URL or show an administrator request as a restricted-user test.
Check where the grant comes from

This retained account has the User group and role. Your custom test account must show the intended assignment instead. Write down each direct and inherited source before testing: otherwise a second grant can make an operation succeed even after the role you are inspecting was restricted. The linked employee below is a staff relationship, not another permission grant.
10. Prove allowed work and denied boundaries
Sign the colleague out and back in after changes, or use the supported identity-refresh route. Confirm account and organization. Open Operations → Customers & Benefits through its permitted menu. Inspect the controlled customer, make an allowed non-sensitive edit through its actual editor, save and reopen. Create and reopen a disposable customer only with all required fields and in the training organization.
Attempt deletion only on that disposable record and inspect its existence afterward from the administrator session. Test a restricted screen using its actual copied URL in the colleague session as well as checking the menu. Hidden navigation does not alone establish route or API protection.
Capture account, organization, role sources, action, intended result, actual response and saved-state check. Keep optional page, approval and mobile tests tied to the product, role and module that implement them. A missing workflow cannot prove approval is denied; an unavailable feature cannot prove menu authorization works.

Read a denial precisely: this historical fixture reports that /operations/hubs is not available for the role. It shows the route that was refused and an optional Request access control. It is not proof that your new role denies deletion of a customer; that requires the operation-specific check described above. Nor should this old owner-access finding be copied as a desired Owner policy. If an intended action is refused, give the administrator the exact route and current account context.
11. Remove access and maintain shared roles
Remove the colleague's explicit group membership and save. Remove any separate direct editor grant through the eligible profile Remove action or the authorized API. Reopen the profile, refresh the colleague's session and repeat the same record, route and action checks.
Why this matters
We're removing the source of access, then repeating the same test. If access remains, we'll check the other roles and groups before changing unrelated controls.
Removing a business role does not lock the account or revoke every device. If a new responsibility applies to only part of a group, create a separate role/group rather than broadening the shared role for everyone. A renamed role identifier requires a replacement role and deliberate assignment migration; existing Name is immutable. Test the replacement before withdrawing the old grant, then repeat denied operations to catch privileges the old role contributed.
Limitations and checks
Why this matters
A useful permission profile lets the intended work succeed and makes its boundaries predictable. Keep records, components and menus distinct, trace every assignment source, and verify changes through the person's own refreshed session.
Source review does not establish backend enforcement, mobile results or immediate session propagation. Preserve any failed restriction as an application finding; do not edit it into a successful course outcome.
BusinessMade result verification
Confirm the ordinary colleague can open the intended BusinessMade route in a fresh session and complete the authorized record operation. Test denied routes separately from hidden menus. Check the linked HR employee without assuming it is the login account. A branch selector is not a substitute for data authorization. BusinessMade source entries: packages/ui/src/ui/sidebars/business-made-links.ts, apps/business-made/src/shell/route-registry.ts.
BusinessMade Password Policy: Rules, Assignments and Self-Service Access — supporting guide
BusinessMade entry: Admin → Password policy (/admin/password-policy).
Use a controlled staff login and retain another administrator while changing password rules. A password policy is separate from an employee clock-in passcode or a Device Hub connection credential.
Scope: This BusinessMade route uses the shared component whose complete procedures follow. Use the BusinessMade menu and organization throughout. Shared references are implementation evidence, not instructions to switch products. These written steps have not been replayed as a new BusinessMade live walkthrough.
What you will configure
BusinessMade Password Policy combines password requirements with who may change or reset their password. We will create a controlled policy, assign it and test which policy applies, without experimenting on the only administrator account.
1. Create the requirements
The policy record holds constraints; an assignment makes those constraints relevant to a person. Keep a separate administrator available during testing.
Open Admin → Password policy. In the policy list below the assignments panel, use the add control to create the record. Use a recognizable training name such as course-staff-policy and keep it separate from your active default.

Historical empty-list capture, despite its filename: this is not a policy editor or an assigned policy. Current source adds Who each policy applies to above the list. A fresh form, saved assignment and effective-password result are still missing from the course evidence.
Enter Name and Description. Set the intended password age in days, reset delay in minutes, failure limit, dictionary allowance, minimum length (the source field is minLenght), lowercase, uppercase, number and symbol requirements, Pattern and excluded characters. Inspect History Age before setting it: this schema provides no unit explanation, so do not invent one. Save and reopen the exact policy.
Check the result: Requirements persist; enforcement is not claimed until exercised through an actual password flow.
2. Control self-service and assign the policy
Person assignments take precedence over group, then role, then the organization default. With no policy the interface states people can change and reset their own passwords.
Set People can change their own password and People can reset a forgotten password deliberately. Use Organisation default only when the policy should cover those without a more specific assignment. In Who each policy applies to, locate the saved policy by name. Choose People, Groups or Roles, choose the controlled target in Choose…, then select Apply this policy. Wait for the response; this assignment has its own save action and does not wait for a policy-form Save. Refresh and inspect that target under the policy. Recheck an explicitly assigned person when also testing a group or role policy.
Check the result: The intended assignment is returned by the server and effective precedence is checked.
3. Test password change and recovery
Disabling forgotten-password reset means no reset is sent for people under that policy. Completing a temporary-password sign-in is described as still allowed; do not confuse that exception with unrestricted self-service.
In the controlled account attempt a password that violates one configured requirement, read validation, then use an allowed new password. Sign out and sign in again to prove the change. Test Forgot password with the controlled inbox only when reset is enabled. When testing reset disabled, show the actual user-facing outcome and confirm the policy with the administrator rather than repeatedly sending requests. Do not show passwords or reset tokens in recording.
Check the result: The new password works and the recovery behavior matches the effective policy.
4. Replace an assignment and recover
Removing an explicit policy can expose a group, role or default policy underneath it; it does not necessarily mean no restrictions.
In Who each policy applies to, remove the controlled target with the Remove cross next to its chip. To replace it instead, choose that target under the replacement policy and select Apply this policy. The chooser indicates an existing assignment with “now …”; inspect that before replacing it. Refresh. Repeat the effective-policy check using the same controlled account. If policy retrieval fails use the displayed Retry/Refresh action; do not save an empty replacement over missing data. Restore the original controlled assignment after the exercise.
Check the result: Fallback and restoration are verified without locking out the administrator.
Troubleshooting and recovery
Read the actual error and inspect persisted state before retrying a create or other write. Keep the selected organization, record and operation visible. A saved configuration, permission, provider connection and working consumer are separate checks; verify the one the lesson claims. Reopen after saving and compare a controlled alternate/failure path where the chapter calls for it. If the consumer does not behave as expected, retain the error and the saved record identity before changing more fields.
Check your result
You can now follow the module’s setup and check its result. Use the relevant chapter for an alternative, and verify the actual consumer before treating configuration as complete.
Limitations and checks
Current assignments component and SDK PasswordPolicySchema inspected. Exact backend enforcement of every numeric/pattern field needs controlled live tests. History Age lacks a clear unit in the schema; record as a UI documentation gap, not a guessed instruction. No passwords, assignments or email were changed here.
BusinessMade routing and outcome check
The menu and route were checked in packages/ui/src/ui/sidebars/business-made-links.ts and apps/business-made/src/shell/route-registry.ts. Open the module through the route stated at the start, perform the controlled procedure, save, reopen and inspect its actual BusinessMade consumer. Do not infer branch isolation from a header location selection when this shared screen reads organization-wide records. Record any access refusal or consumer mismatch with the exact record identity. No new provider, payment, physical-device or live-tenant action was performed for this adaptation.